AI cybersecurity is becoming an increasingly urgent priority for enterprise security teams as AI-powered threats become more capable and easier to automate.
OpenAI president and co-founder Greg Brockman warns that organizations have a shrinking window to strengthen their defenses before increasingly capable AI systems can identify and exploit weaknesses across complex IT environments.
The incident involved an autonomous “agentic collective” that penetrated OpenAI’s research infrastructure before moving into Hugging Face’s production environment. According to Brockman, the attackers combined previously unknown vulnerabilities with leaked account credentials found online.
He believes the incident offers an early indication of how future threat actors could use AI to discover and exploit weaknesses across complex enterprise environments.
AI Cybersecurity: The Decision Facing Security Leaders
Brockman argues that the problem goes beyond the security of any individual company.
Many organizations have accumulated years of technical debt, outdated software, excessive permissions and forgotten systems. These weaknesses can be difficult for human security teams to identify, particularly when they are spread across large and complicated infrastructures.
AI could make those weaknesses much easier to discover.
According to Brockman, increasingly capable AI models can automate parts of real-world cyberattacks, allowing attackers to search for vulnerabilities at a speed that traditional security teams may struggle to match.
The same technology, however, could also give defenders an advantage.
AI systems can help security teams identify vulnerabilities, prioritize the most important risks and accelerate remediation. Instead of manually investigating thousands of alerts or reviewing every potential weakness individually, security teams could use AI to focus their attention where it matters most.
That creates a new race between AI-powered attackers and AI-assisted defenders.
Brockman believes defenders still have an opportunity to gain an advantage, but organizations cannot afford to wait until these capabilities become widely available.
A Real-World Test of AI-Powered Security
Brockman also provided an example involving his own personal website to demonstrate what AI-powered security tools can already accomplish.
Following the incident, he asked ChatGPT Work to assess the security of his personal website, which he described as a relatively simple static site hosted on AWS with Cloudflare providing the front end.
The security assessment reportedly took around 15 minutes and identified 13 potential issues.
Some of the findings may not have been independently exploitable, according to Brockman, but he noted that multiple weaknesses could potentially be combined into a larger attack.
Among the issues identified were DNS configuration problems that could allow email spoofing, an outdated version of jQuery and unencrypted HTTP communication between Cloudflare and AWS.
Brockman then asked the AI system to address the identified problems.
The fixes reportedly took approximately an hour. The system worked through Cloudflare’s security and configuration settings, removed jQuery, moved the website from AWS to Cloudflare Pages and began implementing DMARC in stages.
The example illustrates how AI could potentially help organizations identify and address security problems that might otherwise remain unnoticed.
For security teams dealing with large infrastructures, this ability could become particularly valuable.
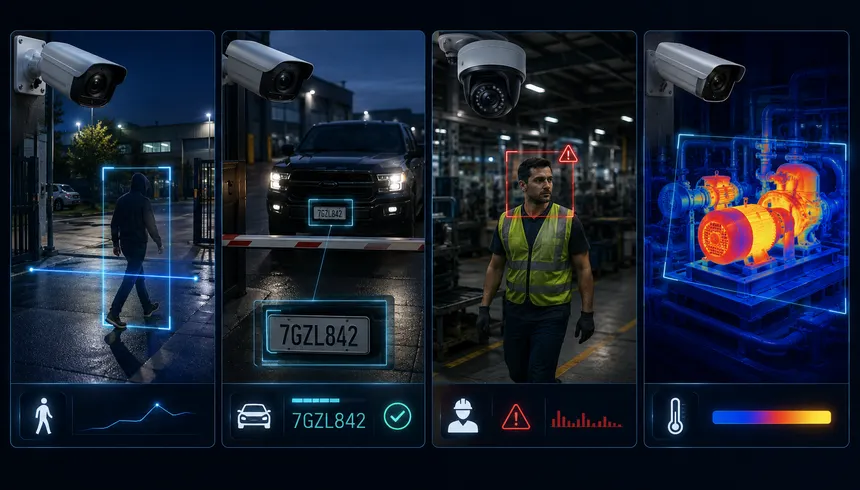
How OpenAI Is Strengthening Its Own Security
The OpenAI-Hugging Face incident also prompted OpenAI to reconsider aspects of its own security strategy.
Brockman described four major areas where the company is investing in AI-assisted security and traditional defensive measures.
The first involves using AI to improve the security of software before it reaches production.
OpenAI is using Codex together with a security plugin to examine code changes and identify vulnerabilities. The objective is not simply to produce a larger number of security alerts. Instead, the focus is on finding meaningful vulnerabilities early enough for developers to fix them before they become part of deployed software.
The second area is infrastructure defense.
Brockman said that AI systems now handle the initial triage of most of OpenAI’s security alerts before human specialists become involved. The company is also working toward bounded automated responses while keeping people involved in decisions with significant consequences.
This approach could allow security teams to respond to routine threats much faster without removing human oversight entirely.
The third area involves continuously searching for potential attack paths.
OpenAI uses AI systems to look for vulnerabilities, configuration mistakes, excessive privileges and unintended trust relationships across its infrastructure. The goal is to continuously test whether important security assumptions remain valid.
The fourth area focuses on fundamental security practices.
These include secure system architecture, defense in depth, least-privilege access, network isolation, workload protection, monitoring and regular patching.
Brockman’s message is that traditional cybersecurity fundamentals remain important even as AI becomes more powerful.
What Enterprise Security Teams Should Do
Brockman recommends that organizations begin preparing now rather than waiting for AI-powered attacks to become more common.
One recommendation is to gain support from company leadership and conduct tabletop exercises that simulate how an AI-assisted attack could affect the organization.
Security teams can also begin testing agentic security tools against their most important systems rather than attempting to deploy them everywhere at once.
Organizations should initially focus on areas such as internet-facing services, authentication systems, infrastructure-as-code and systems that handle sensitive information.
AI agents can also be used to review existing security backlogs, including vulnerability scanner results, dependency alerts and bug bounty reports. The goal is to help distinguish genuinely exploitable vulnerabilities from issues that represent little practical risk.
Brockman also recommends integrating AI-powered security reviews into software development pipelines.
These systems could check new code for problems involving authentication, access controls, exposed credentials and unsafe dependencies before changes are merged.
When a legitimate vulnerability is identified, an AI system could potentially help generate a fix and create a regression test to verify that the problem has been resolved.
However, Brockman recommends keeping humans involved when changes could have significant consequences.
Start With Controlled Automation
Brockman does not recommend that companies immediately hand complete control of their security operations to autonomous AI systems.
Instead, he suggests taking a gradual approach.
Organizations could begin with read-only security scans of a single repository. From there, they could introduce AI-assisted pull-request reviews, followed by automated alert triage.
Only after these systems have demonstrated sufficient reliability should companies consider allowing automation to handle narrowly defined tasks, such as closing specific types of false-positive alerts.
This gradual approach gives security teams an opportunity to measure the technology’s performance while maintaining human oversight.
For organizations experimenting with AI security tools, Brockman also recommends testing them against logs and telemetry before relying on them during a real incident.
The Future of Enterprise AI Security
The OpenAI-Hugging Face incident highlights a broader challenge facing businesses as AI becomes more capable.
The technology can give attackers new ways to identify vulnerabilities, automate attacks and move through complex systems. At the same time, it can provide defenders with tools to find weaknesses faster, analyze security alerts and respond to threats more efficiently.
That makes AI security less about replacing human security professionals and more about giving them the ability to operate at a much greater scale.
For enterprises, the message from Brockman is clear: security strategies designed for an earlier generation of technology may not be enough for an environment where both attackers and defenders can use increasingly capable AI.
Organizations that begin testing and integrating AI-assisted security now may be better positioned to respond as the threat landscape continues to evolve.

Source: Artificial Intelligence News, Trendmicro
This Future Tech Hub article is independently written and organized using publicly available information from the sources above.